An Efficient Framework for Secure Data Sharing in Cloud Computing Environments
DOI:
https://doi.org/10.65521/ijacte.v6i1.4592Keywords:
Abstract
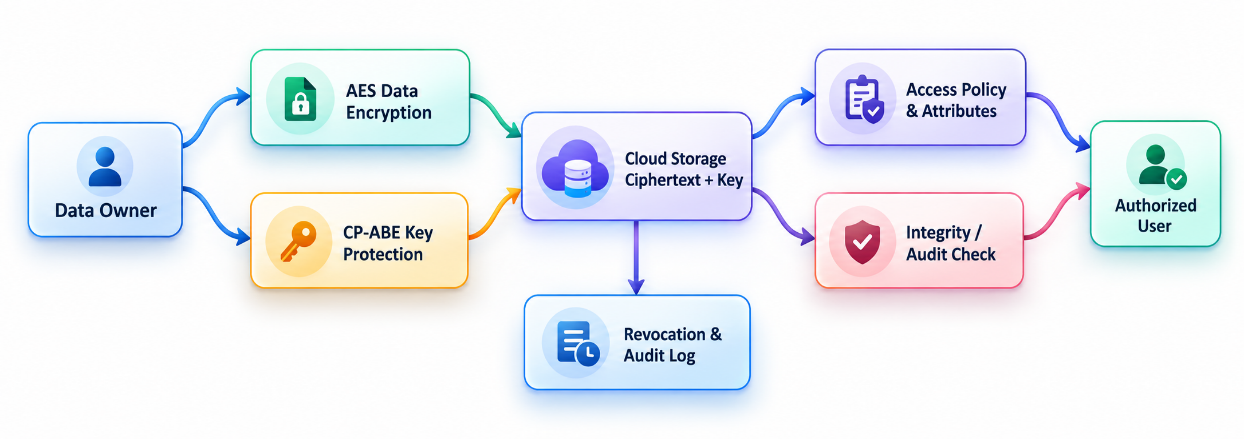
Cloud computing provides scalable storage and collaboration, but outsourced data sharing creates concerns about confidentiality, unauthorized access, key management, user revocation, and integrity verification. This methodology paper proposes an efficient secure data-sharing framework that combines symmetric encryption for bulk data, ciphertext-policy attribute-based encryption (CP-ABE) for fine-grained key protection, cryptographic integrity verification, controlled revocation, and auditable access logging. The design follows a semi-trusted cloud model in which the cloud may store and process encrypted objects but is not allowed to learn plaintext content or user secret keys. A stepwise methodology is defined for system setup, data encryption, policy binding, cloud upload, authorized retrieval, integrity checking, and revocation. The framework is evaluated analytically using confidentiality, access-control precision, integrity, privacy, revocation, and computational-overhead criteria. The analysis indicates that separating data encryption from policy encryption can reduce repeated expensive public-key operations while maintaining cryptographic access control. The resulting framework is suitable as a reproducible foundation for secure cloud file-sharing prototypes and comparative experiments using literature available up to 2017.