An Efficient Data Encryption Framework for Secure Cloud Storage Systems
Keywords:
Abstract
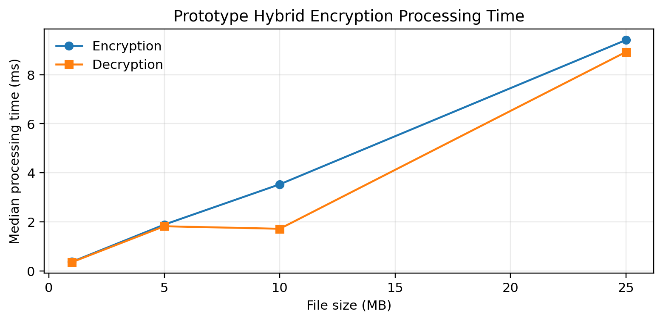
Cloud storage reduces local infrastructure cost and improves data availability, but outsourcing sensitive information to infrastructure outside the data owner’s direct control creates persistent confidentiality, integrity, and access-control risks. This paper presents a methodology for an efficient hybrid data-encryption framework designed to secure files before they are transferred to cloud storage. The framework separates bulk-data encryption from key protection: file contents are protected with AES-256 in Galois/Counter Mode (AES-GCM), while the per-file symmetric key is wrapped with RSA-2048 using OAEP. Authenticated encryption detects unauthorized ciphertext modification, and an independent policy/key service prevents the cloud-storage provider from receiving plaintext encryption keys. Fine-grained authorization concepts are incorporated at the key-release layer so that storage access and decryption permission are treated as separate decisions. The evaluation methodology combines security-property analysis with a reproducible prototype benchmark across 1, 5, 10, and 25 MB files. Results show nearly linear processing time with file size and negligible storage expansion because public-key cryptography is applied only to the small data-encryption key. The framework therefore provides a practical balance between confidentiality, integrity, controlled key distribution, and computational efficiency for cloud storage applications.