An Efficient Intrusion Detection System Using Data Mining Techniques for Network Security
Keywords:
Abstract
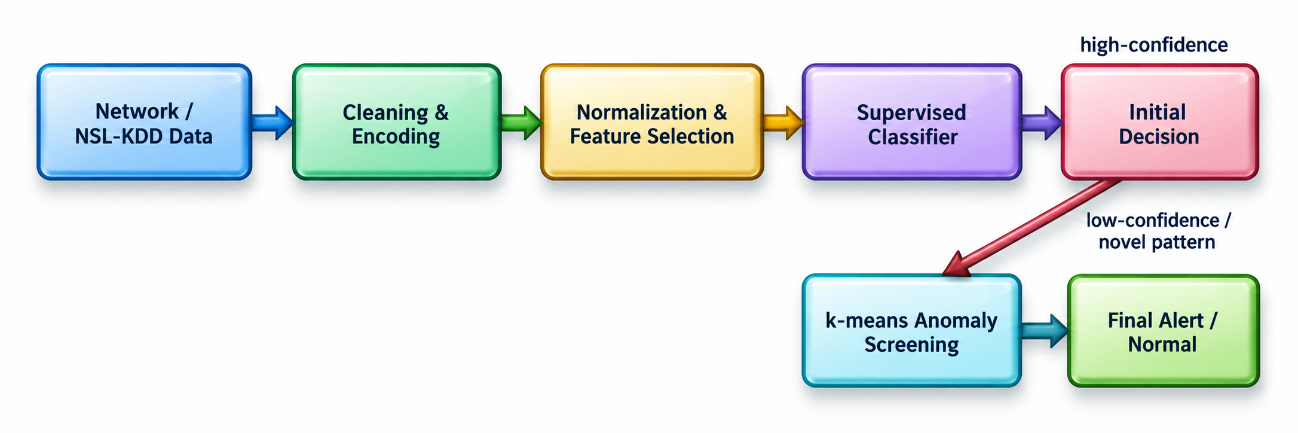
Intrusion detection remains an essential second line of defense when preventive mechanisms such as authentication, access control, and firewalls are unable to identify every malicious activity. This methodology paper proposes an efficient network intrusion detection framework that combines data preprocessing, feature selection, supervised classification, and an anomaly-screening stage based on data mining. The framework is designed for benchmark evaluation on the NSL-KDD data set, which was introduced to reduce important redundancy and evaluation problems in KDD Cup 99 [7]. Categorical traffic attributes are encoded, numeric attributes are normalized, and redundant or weak predictors are removed before classification. A Random Forest model is used as the primary classifier because ensemble trees can provide strong generalization and feature-importance estimates [13], while low-confidence records are forwarded to a k-means anomaly-screening stage. Decision Tree, Naive Bayes, k-nearest neighbor, and Support Vector Machine models are retained as baselines because these techniques have established use in intrusion detection research [3]-[5], [14]. Performance is assessed by accuracy, detection rate, precision, F1-score, false-positive rate, and ROC-oriented measures [15]. The proposed methodology emphasizes a practical balance among detection capability, false alarms, computational efficiency, and interpretability. Results are presented as a benchmark-oriented methodological evaluation supported by published studies through 2015, avoiding unsupported claims of a newly deployed system. The framework is suitable for reproducible academic testing and can be extended to multiclass attack categorization and online traffic streams.