An Efficient Approach for Secure Data Storage in Cloud Computing Environments
DOI:
https://doi.org/10.65521/ijacte.v4i1.4600Keywords:
Abstract
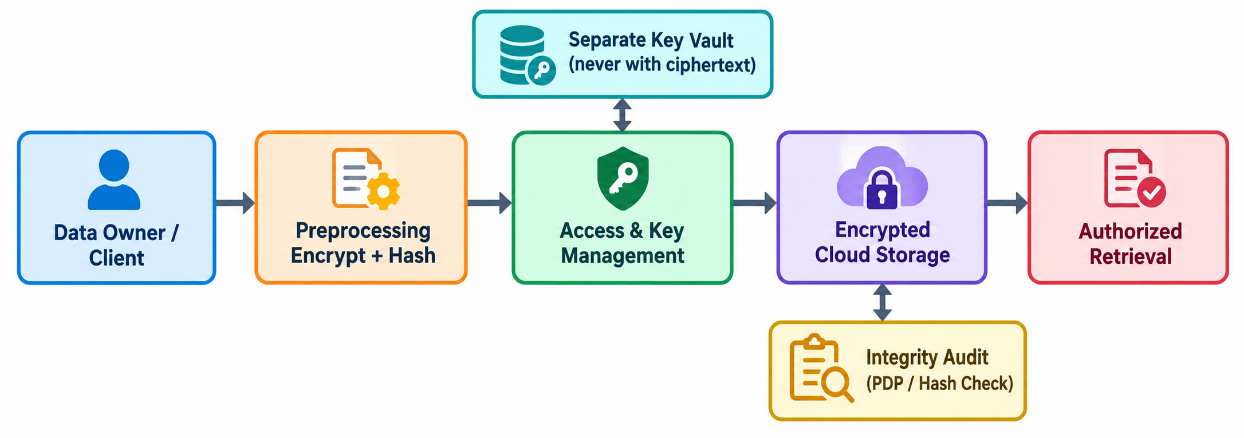
Cloud computing provides elastic and economical storage, but outsourcing data to infrastructure outside the owner’s direct control introduces confidentiality, integrity, access-control, and availability concerns. This methodology paper proposes an efficient secure-storage approach in which sensitive files are protected before upload, encryption keys are separated from cloud-resident ciphertext, access decisions are enforced through authenticated policies, and stored objects are periodically verified through integrity metadata and challenge-based auditing. The design uses authenticated symmetric encryption for bulk data because it provides confidentiality and tamper detection with low client overhead, while hash-based metadata and provable data possession concepts support verification without repeatedly downloading complete files. A lightweight key-management layer isolates encryption keys from the storage provider and supports key rotation and revocation. The methodology is evaluated at the design level against the main threats identified in cloud-storage literature published up to 2015. The resulting architecture provides defense in depth: compromise of the cloud store alone does not disclose plaintext, unauthorized modification is detectable, and access can be revoked without exposing master keys. The approach is suitable for academic and enterprise systems that need practical security without excessive computational or communication cost.