BehaviorGuard-AI: A Context Aware UEBA Framework for Insider Threat Detection Using Unsupervised Behavioral Analytics
Keywords:
Abstract
Insider threats are especially difficult to detect because they come from legitimate users with authorized access, and traditional defences which are mainly tuned to detect external attacks, often miss the subtle behavioral deviations exhibited by insiders. This paper presents BehaviorGuard-AI, a context aware UEBA framework that detects anomalous user behavior using behavioral analytics and unsupervised learning. The system builds meaningful baselines through attributes like contextual user profiling, engineered behavioral features, shift based segmentation, and role aware peer grouping. A hybrid detection pipeline combines HDBSCAN clustering with Isolation Forest validation to surface rare or unusual patterns in large scale enterprise authentication logs.
BehaviorGuard-AI provides investigative depth beyond statistical anomaly scores with an Email Compliance Auditing Pipeline. This pipeline detects high risk users by anomalies and correlates their email activity to anomalous windows in time and applies heuristic threat filters and Retrieval Augmented Generation (RAG) workflow to evaluate potentially sensitive messages against organizational policy. The system narrows down the workload and cuts down on the computational cost by confining the email analysis to the windows flagged as anomalous, while providing policy relevant context for analysts.
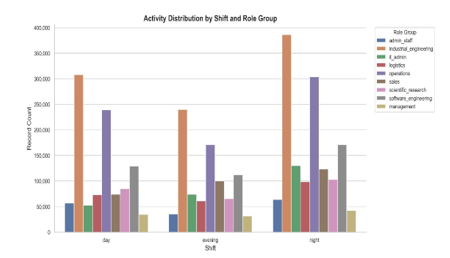
The framework was evaluated on a synthetic enterprise data set containing more than 3.3 million user activity records per hour and ten engineered behavioral features. The system identified 2,764 behavioral clusters and labeled approximately 6.34% of observations as anomalous without any labeled threat data. Results suggest that combining behavioral anomaly detection with targeted and policy aware email auditing provides analysts with a combination of clear anomaly signals and actionable context that improves the effectiveness of insider threat investigation.
Downloads
Published
How to Cite
Issue
Section
License

This work is licensed under a Creative Commons Attribution-NoDerivatives 4.0 International License.