Hybrid Data Mining-Based Intrusion Detection Framework for Network Security
DOI:
https://doi.org/10.65521/ijaece.v4i1.4314Keywords:
Abstract
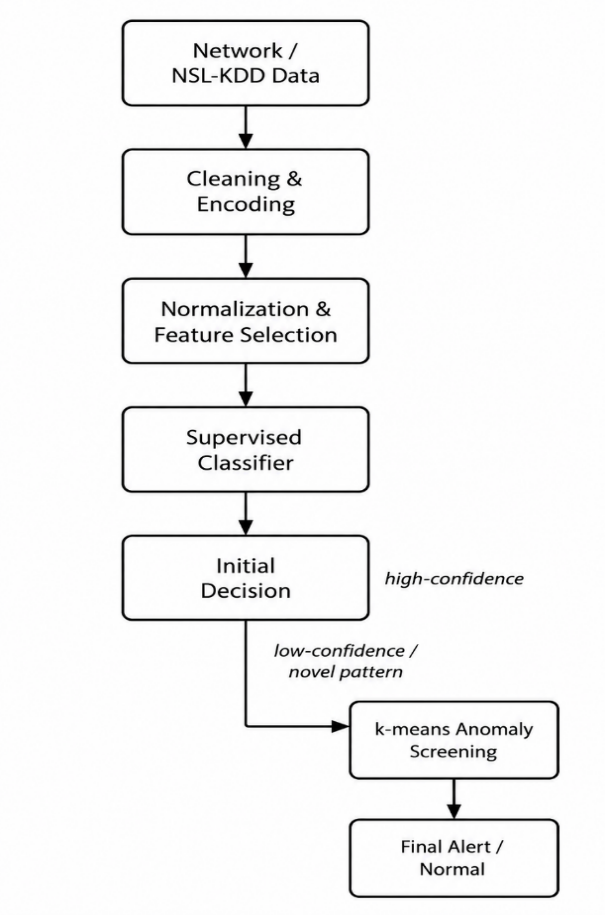
The increasing complexity of network attacks has created a need for intrusion detection methods that can identify malicious traffic accurately while maintaining a low false-alarm rate. This paper presents a hybrid data mining-based intrusion detection framework for network security that integrates preprocessing, feature selection, supervised classification, and anomaly screening within a unified detection process. The NSL-KDD dataset is used as the benchmark environment for evaluating the proposed methodology. Categorical network attributes are encoded, numerical features are normalized, and weak or redundant attributes are removed to improve classification efficiency. Random Forest is employed as the primary supervised classifier because of its ability to handle high-dimensional network data and provide feature-importance information. Network records with low classification confidence are further examined using k-means clustering to identify suspicious traffic patterns that may not be clearly separated during the initial classification stage. Decision Tree, Naive Bayes, k-nearest neighbor, and Support Vector Machine techniques are used as baseline models for comparative evaluation. Performance is assessed using accuracy, detection rate, precision, F1-score, false-positive rate, and ROC-based measures. The hybrid framework is designed to combine the strengths of supervised learning and unsupervised data mining in order to improve detection reliability and reduce unnecessary false alarms. The methodology provides a reproducible basis for evaluating intrusion detection approaches and can be extended to multiclass attack recognition and real-time network monitoring environments.