A Secure Cloud-Based Framework for Data Storage and Access Control in Smart
DOI:
https://doi.org/10.65521/ijeecs.v9i1.4514Keywords:
Abstract
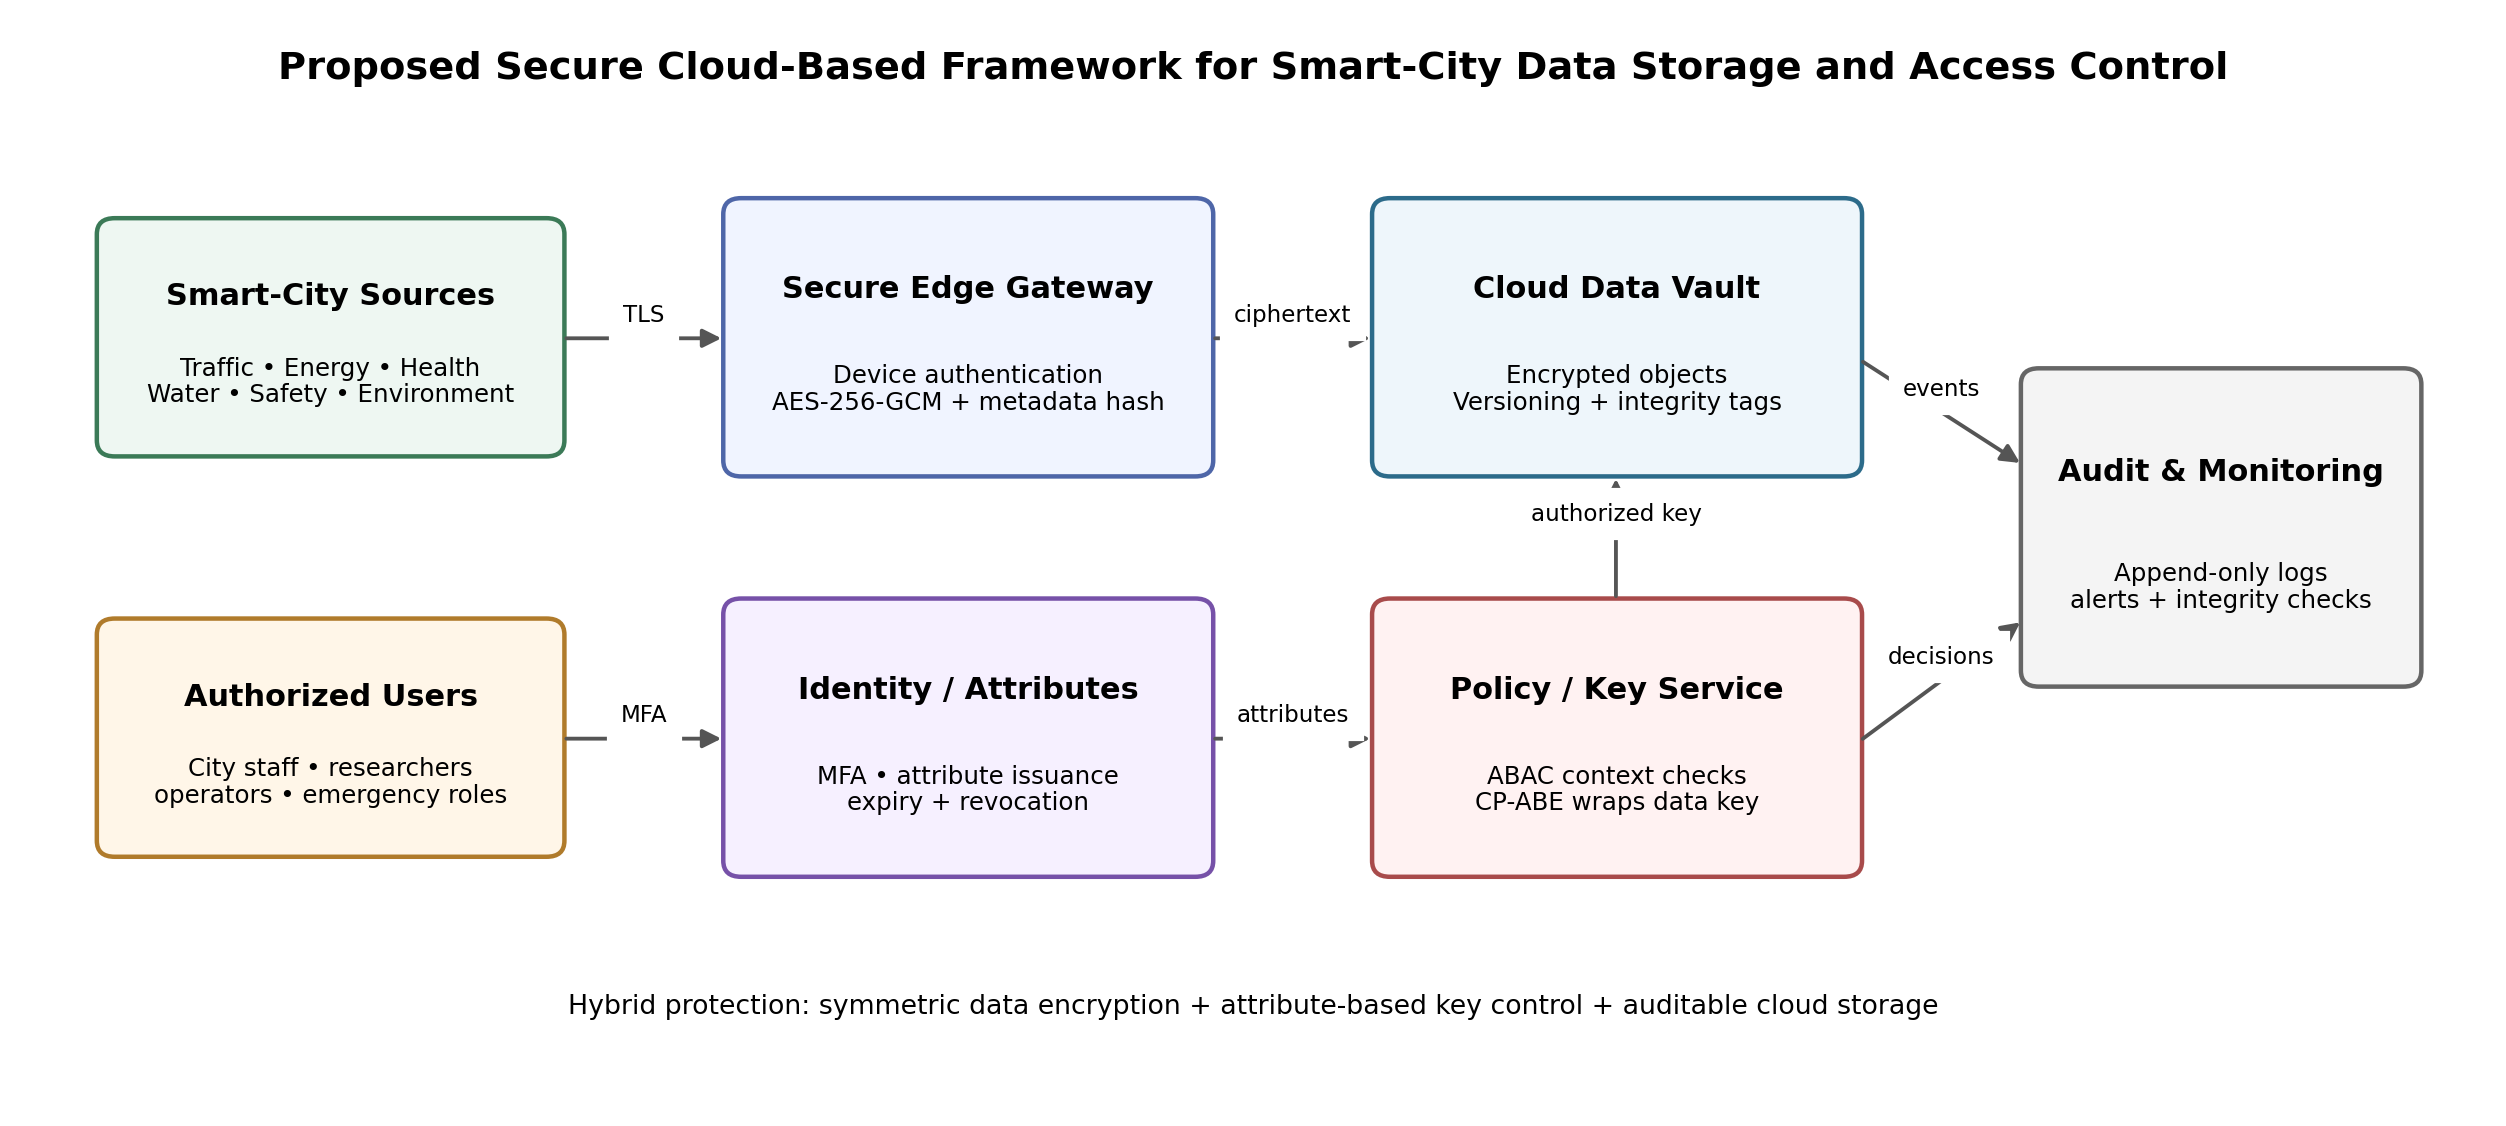
Smart-city platforms continuously collect sensitive information from traffic systems, energy meters, environmental sensors, public-safety infrastructure, health services, and citizen applications. Centralized cloud storage offers elasticity and availability, but it also expands the attack surface and places valuable municipal data outside the direct physical control of data owners. This methodology paper proposes a secure cloud-based framework that combines authenticated edge gateways, AES-256 data encryption, ciphertext-policy attribute-based encryption (CP-ABE) for protected key distribution, attribute-based access control, multi-factor authentication, revocation, and integrity auditing. The framework is designed for heterogeneous smart-city domains in which users require different privileges according to role, organization, location, purpose, and emergency status. A controlled synthetic benchmark is defined to evaluate encryption latency, access-decision delay, storage overhead, revocation behavior, and resistance to unauthorized requests. The methodology emphasizes confidentiality, integrity, least privilege, scalability, and auditable accountability while keeping intensive cryptographic operations away from resource-constrained sensors. The proposed design provides a practical basis for testing secure urban data sharing without requiring the cloud provider to be fully trusted.