A Secure Cloud-Based Framework for Distributed Data Storage and Access Control
DOI:
https://doi.org/10.65521/ijacte.v8i1.4635Keywords:
Abstract
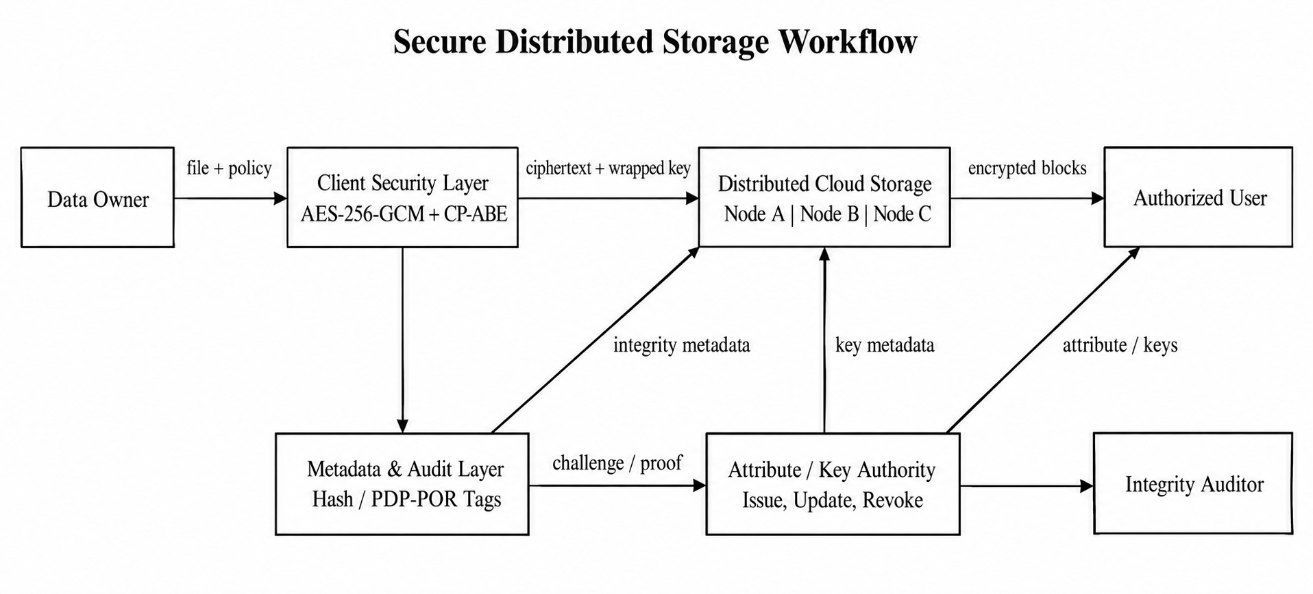
Cloud storage offers elastic capacity and convenient data sharing, but outsourcing sensitive information to remote infrastructure introduces risks related to confidentiality, integrity, availability, and authorization. This methodology paper proposes a secure cloud-based framework that combines client-side symmetric encryption, ciphertext-policy attribute-based encryption (CP-ABE), distributed storage, integrity verification, and revocation-aware access control. Data are encrypted with AES-256-GCM before leaving the client, while the symmetric data key is protected by a CP-ABE policy so that decryption depends on user attributes rather than a single account identity. Encrypted blocks are distributed across independent storage nodes with replication, and cryptographic hashes together with proof-of-possession/retrievability concepts are used to support integrity checking. The methodology defines system entities, threat assumptions, upload and access workflows, revocation procedures, auditing, and a prototype evaluation procedure. A small local benchmark shows near-linear cryptographic processing as file size increases, while functional tests demonstrate that unauthorized attributes, modified ciphertext, and revoked credentials are rejected. The framework therefore provides a practical layered design for secure distributed cloud storage without requiring the cloud provider to learn plaintext data or hold unrestricted decryption keys.