Blockchain-Enabled Secure Data Sharing Architecture for Cloud Computing Environments
DOI:
https://doi.org/10.65521/ijacte.v11i1.4114Keywords:
Abstract
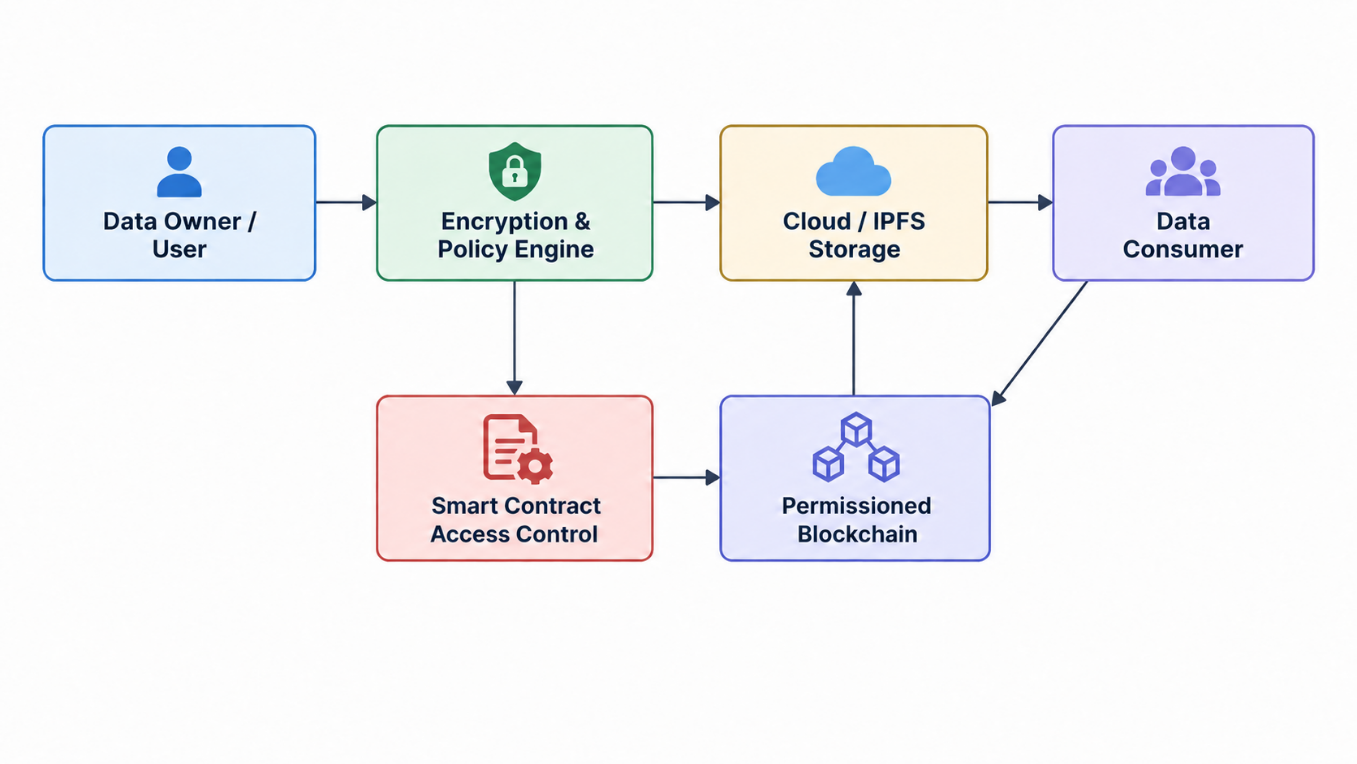
Cloud computing provides scalable storage and computing services, but centralized authorization, opaque audit trails, and dependence on a cloud service provider can complicate secure inter-organizational data sharing. This methodology paper proposes a blockchain-enabled architecture in which large encrypted files remain in cloud or InterPlanetary File System (IPFS) storage while blockchain records store content hashes, access-policy references, identity assertions, consent events, and immutable audit logs. Smart contracts enforce authorization decisions and support revocation, while attribute-based encryption supplies fine-grained cryptographic protection. The design follows a permissioned blockchain model to reduce the latency and cost associated with public-chain consensus. A controlled analytical evaluation is defined using access latency, transaction throughput, integrity-verification rate, unauthorized-access rejection, storage overhead, and auditability as performance indicators. The methodology predicts that the hybrid on-chain/off-chain structure can strengthen integrity, accountability, and cross-domain trust without placing bulk data on the ledger. The framework is intended as a reproducible basis for prototype implementation in enterprise, healthcare, education, and research-cloud environments.