A Secure Data Transmission Framework for Cloud-Based Communication Systems
Keywords:
Abstract
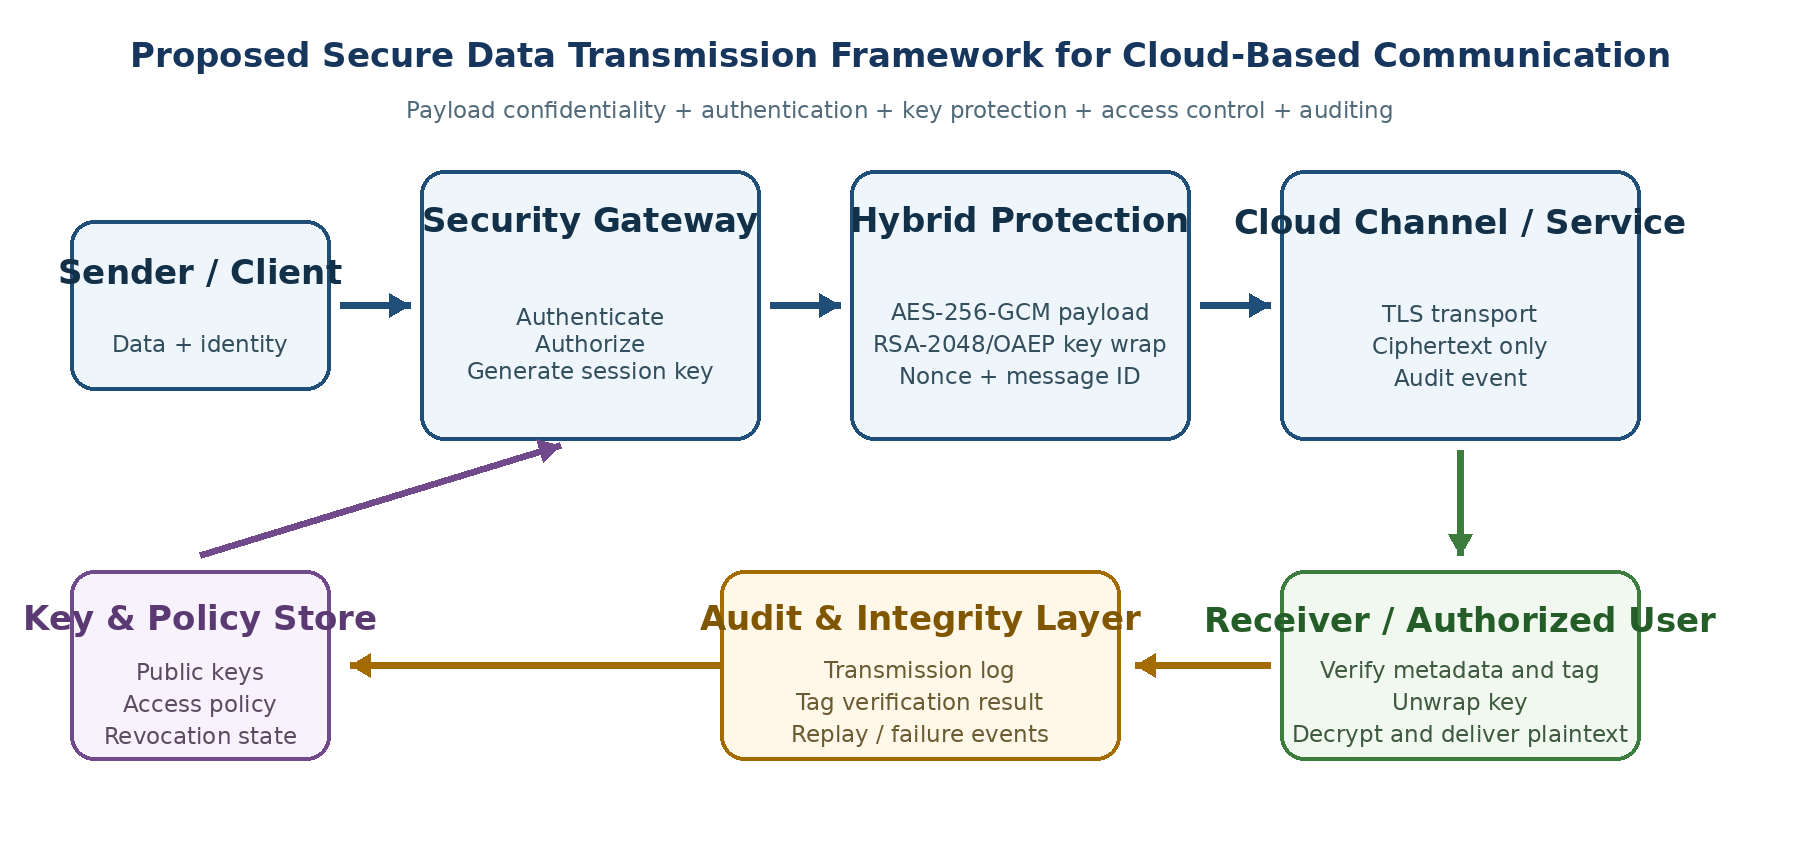
Cloud-based communication allows organizations to exchange and process data through elastic, shared infrastructure, but it also extends the security boundary beyond the direct control of the data owner. This paper presents a methodology for a secure data transmission framework that protects confidentiality, integrity, authenticity, and controlled access across client-to-cloud and cloud-to-client communication. The framework combines authenticated symmetric encryption for bulk data, asymmetric encryption for session-key protection, identity and policy verification, replay-resistant metadata, and audit logging. The design is motivated by established cloud-security concerns including multi-tenancy, outsourced storage, insecure interfaces, cross-domain trust, and loss of direct data possession [1]-[5]. A controlled prototype was used to measure the cryptographic overhead of AES-256-GCM with RSA-2048/OAEP key encapsulation for 1 MB, 5 MB, and 10 MB payloads. The measured results show millisecond-level encryption/decryption cost on a modern x86-64 platform, while ciphertext expansion remains negligible for ordinary file transfers. Tamper tests also show that modified ciphertext is rejected by the authenticated-encryption layer. The resulting methodology provides a practical, layered approach suitable for cloud messaging, file exchange, and service-to-service communication where security must remain independent of the trustworthiness of the transport or storage provider.